 Follow Us on Google News


 Follow Us on Google Discover
This article is part of The Guardian’s Special Focus on Nigeria’s Leading and Reliable Data Protection Compliance Organisations Championing Privacy, Compliance and Digital Trust
As Nigeria’s digital economy expands, protecting personal information has become a critical responsibility for organisations across the public and private sectors. From financial transactions and healthcare records to employee information and online services, personal data now plays a central role in how institutions operate, make decisions and serve their customers. Yet, as the volume of information collected and processed continues to grow, so do the risks associated with its misuse, exposure and inadequate protection. Addressing these challenges requires more than an understanding of regulatory requirements. It demands sound legal knowledge, effective governance, practical risk management and a sustained commitment to building public trust.
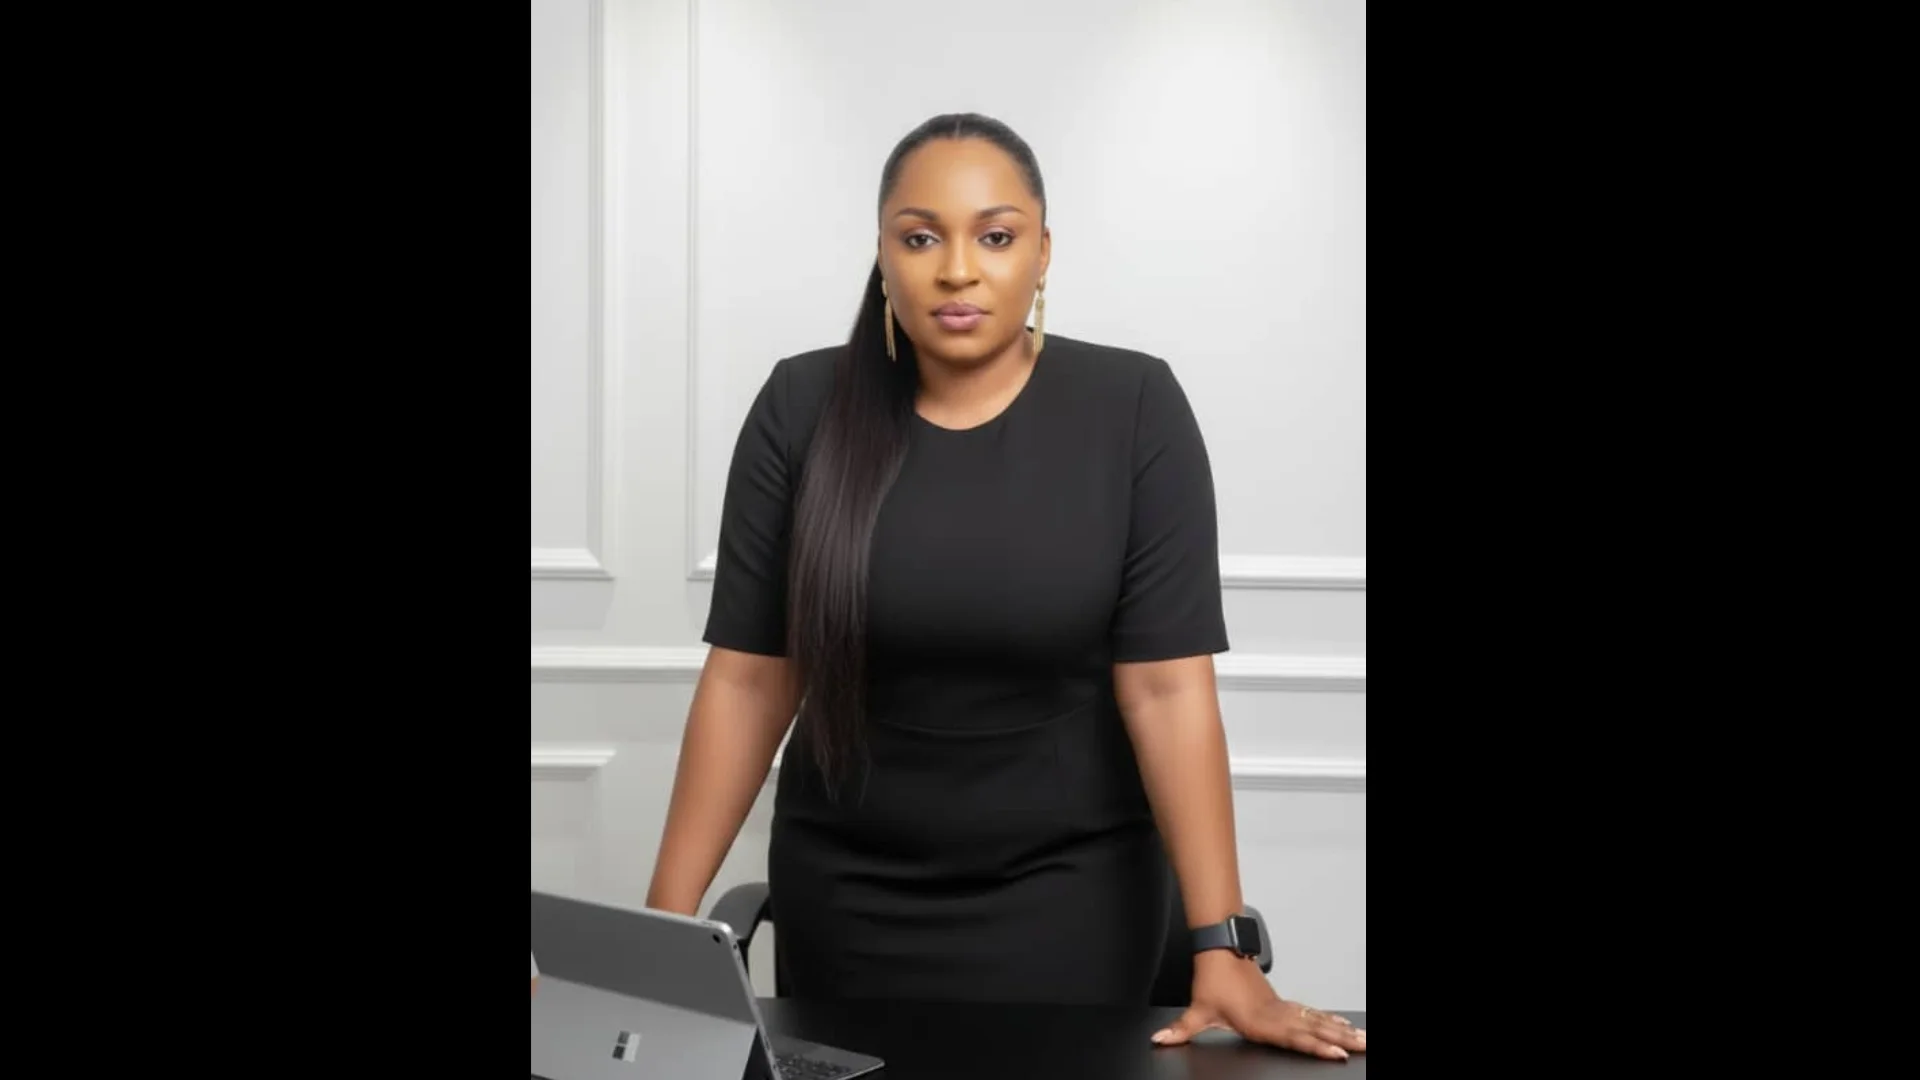
For Ifeoma Peters, Managing Partner at DNL Partners and Lead Consultant in Data Protection and Regulatory Compliance, these responsibilities form the foundation of her professional practice. Through legal advisory services, compliance audits, policy development, training and institutional capacity-building, she works with organisations to strengthen their data protection practices and integrate privacy considerations into their operations.
At DNL Partners, Peters leads data protection audit and business development initiatives, helping organisations understand their obligations, identify weaknesses in existing systems and implement measures to address them. Her approach combines legal interpretation with practical solutions designed to fit the realities of different institutions. Rather than treating compliance as a collection of documents, she encourages organisations to establish processes that guide how personal information is collected, accessed, used, stored, shared and eventually disposed of.
Her professional contributions extend beyond individual organisations to initiatives that support the development of data protection policy and regulatory awareness in Nigeria. One of the notable examples is her involvement in the Edo State Digital Policy Project, funded by the Bill & Melinda Gates Foundation. As part of the initiative, she contributed to the development of the Edo State Data Protection Regulation and the Intellectual Property Policy for Public Institutions.
The project addressed important questions about how public institutions should manage information, protect personal data and approach intellectual property within a more digitally connected administrative environment. Developing policies for public institutions requires an understanding of legal requirements as well as the practical circumstances in which government agencies collect, maintain and exchange information. Such frameworks must provide direction while supporting the effective delivery of public services.
Her engagement with regulatory education is equally significant. She developed a training script for the Nigeria Data Protection Commission’s Virtual Privacy Academy, an initiative undertaken through a collaboration between Mastercard and the Nigeria Data Protection Commission (NDPC). The programme contributes to the wider effort to improve understanding of privacy principles and data protection responsibilities among relevant stakeholders.
She has also served on the drafting committee for the Nigeria Data Protection Act General Application and Implementation Directive (NDPA-GAID). Her participation in this process places her among professionals who have contributed to the development of guidance intended to support the application and implementation of Nigeria’s data protection framework.
Her advisory and training engagements have included the Edo State Government, Ogun State Government, the Nigerian Institute of Management and the Institute of Chartered Secretaries and Administrators of Nigeria, among other institutions. These engagements demonstrate the relevance of data protection across different professional and administrative settings. Government agencies, professional bodies and private organisations may handle different categories of information, but all require appropriate procedures for protecting personal data and maintaining accountability.
Peters’ professional development has also been shaped by a combination of legal education and specialised training in information security and governance. She holds an LL.B from Lagos State University, obtained her Bachelor of Laws qualification at the Nigerian Law School, Lagos Campus, and earned an LL.M from the University of Lagos.
Recognising that effective data protection increasingly requires knowledge beyond traditional legal practice, she obtained the ISO/IEC 27001:2022 Lead Auditor qualification after completing relevant training and a skills-based examination. ISO/IEC 27001 provides a framework for establishing, implementing, maintaining and continually improving an information security management system. Knowledge of the standard helps professionals assess whether an organisation has appropriate processes for identifying and managing information security risks.
She has also completed The Definitive GRC Analyst Master Class at Simply Cyber School and an Introduction to Cybersecurity course through Cisco Networking Academy. These qualifications complement her legal background by strengthening her understanding of governance, risk management, information security and the controls that support responsible data handling.
Her professional affiliations include membership of the Nigerian Bar Association, the NBA Section on Business Law and the Digital Rights Lawyers Initiative. She also serves on the Advisory Board of the Data Privacy Lawyers Association of Nigeria (DPLAN). These connections provide opportunities to engage with legal and professional discussions on privacy, digital rights, business regulation and emerging compliance challenges.
At DNL Partners, Peters applies this combined expertise to a range of data protection services. These include compliance audits and regulatory filings, enterprise-wide privacy assessments, gap analysis and remediation, data mapping, policy and procedure development, privacy risk assessments and staff training. The objective is to help organisations understand the information they hold, the purposes for which they use it and the safeguards required throughout its lifecycle.
A typical engagement may begin with examining an organisation’s records of processing activities, privacy notices, internal policies and contractual arrangements with third-party processors. The review may also consider whether the organisation has identified an appropriate lawful basis for processing personal information, established suitable retention periods and created procedures for responding to data subject requests.
Through this work, Peters and her team have conducted and filed more than 100 data protection compliance audits and delivered training to over 100 organisations. These engagements have provided experience across different sectors and organisational structures, where the nature of personal information, operational processes and exposure to risk can vary considerably.
For Peters, the most useful compliance framework is one that employees can follow in practice. Responsibilities should be clear, reporting channels accessible and management oversight consistent. When these elements are established, organisations are better positioned to detect weaknesses early, respond proportionately and demonstrate that privacy is part of everyday decision-making rather than an isolated legal exercise.
Among the persistent challenges Peters identifies are phishing, ransomware, unauthorised access, human error, weak internal controls and inadequate oversight of external service providers. These risks can be intensified by limited public awareness and careless disclosure of personal information on social media. In many cases, the problem is not solely a lack of technology but a failure to establish clear procedures and ensure that people understand how their actions can expose information to harm.
Peters advocates a proactive approach built around understanding what data an organisation holds and who can access it. Appropriate access controls, strong authentication, secure information systems, employee awareness programmes and clear retention and disposal procedures can help reduce exposure. Organisations also need incident response plans that establish how suspected breaches should be reported, assessed, contained and addressed.
She also recognises the importance of effective regulatory oversight. The NDPC has a central role in promoting compliance and holding organisations accountable for their responsibilities. Transparent enforcement and clear communication can help organisations understand the consequences of failing to protect personal information, while encouraging the adoption of better practices across the wider economy. Publicly debated regulatory matters, including the NDPC’s handling of its case involving Meta, illustrate the attention that data protection enforcement can attract and the importance of clarity, accountability and public confidence in regulatory processes.
For Peters, sustainable progress requires cooperation between regulators, organisations, legal practitioners, technology professionals and the public. Individuals need to understand their rights and exercise caution when sharing personal information, while organisations must take responsibility for the systems and decisions through which data is collected and processed. Regulators, in turn, need to provide guidance and apply the law in a manner that supports accountability and confidence in the data protection framework.
Looking ahead, Peters intends to deepen her expertise, expand her work across more sectors and support organisations with increasingly complex data operations over the next three to five years. Her priorities include enterprise-wide privacy assessments, compliance remediation, privacy governance, risk management, practical training and policy development. She also aims to help organisations respond to emerging regulatory requirements and the risks associated with artificial intelligence.
The growing use of AI presents important questions about how personal information is collected, analysed and used to produce automated outputs. Organisations adopting these technologies need to consider what data enters their systems, whether its use is appropriate, how access is controlled and what safeguards are required to address potential risks. These questions make it increasingly important for privacy, legal, governance and technology teams to work together from the early stages of planning and implementation.
DNL Partners’ wider vision is to rank among the world’s first-tier commercial and litigation law firms, guided by innovation, professional excellence and practical business solutions. Within this ambition, data protection and regulatory compliance represent areas where legal expertise can help organisations respond to changing expectations while strengthening their internal governance.
Ultimately, Peters sees data protection as both a legal responsibility and a foundation for trust. People are more likely to engage with organisations when they have confidence that their information will be handled responsibly. For businesses and public institutions, that confidence can support stronger relationships, more accountable operations and a more credible digital presence.
Her work continues to focus on helping organisations move from simply recognising their obligations to putting effective safeguards into practice. As Nigeria’s digital economy develops, the ability to protect personal information will remain an important measure of institutional responsibility. Through legal advisory services, policy contributions, training and practical compliance support, Ifeoma Peters is working to make data protection a meaningful part of how organisations operate, govern themselves and earn the trust of the people they serve.