 Follow Us on Google News


 Follow Us on Google Discover
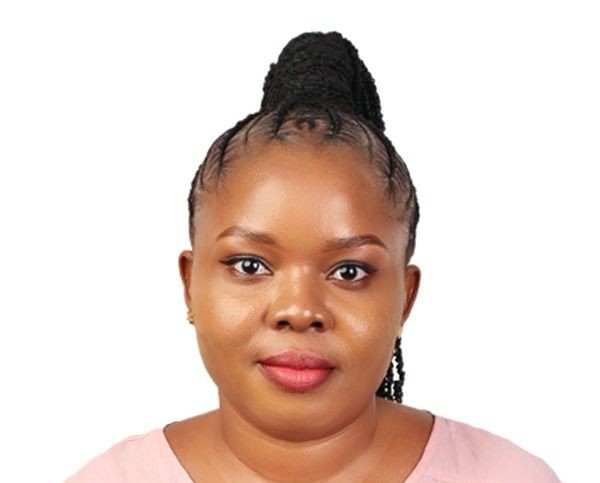
Angela Ukpabi, a risk and compliance financial analyst with experience spanning commercial banking and fintech, has urged financial institutions to adopt risk-based strategies as a frontline defense against the growing sophistication of cyberattacks targeting the sector.
Speaking on the challenge of protecting critical systems in an increasingly digital environment, Ukpabi said static security frameworks and reactive compliance measures no longer offer adequate protection. Instead, she argued for an adaptive approach that prioritises vulnerabilities based on real exposure levels.
“For too long, the financial industry approached digital threats as a compliance exercise — meeting minimum regulatory standards without truly assessing the institution’s evolving vulnerability landscape,” Ukpabi said.
“Risk-based strategies change that paradigm. They evaluate exposure considering internal processes, technology maturity, and the specific threat actors targeting the organisation’s profile. When we do this, we create a security posture that is dynamic, data-driven, and proportionate to the actual risks, not an arbitrary standard.”
She warned that cyber risks shift rapidly, making continuous reassessment essential.
“A phishing vulnerability in January may be a supply chain risk by June, and a ransomware exposure by year-end,” she said.
“Without a risk-based approach that embeds threat modelling, operational resilience testing, and regulatory intelligence into daily operations, institutions find themselves caught off guard.”
Ukpabi highlighted the importance of prioritisation in resource allocation. By mapping assets against potential threats, she said, institutions often find that a small proportion of systems carry the bulk of exposure.
“A well-conceived risk register does more than document problems. When institutions see that 20 per cent of their systems carry 80 per cent of the risk, they can strengthen controls over critical payment gateways, transaction monitoring systems, and sensitive customer data first before spreading budgets thinly across less vulnerable operations.”
She stressed that such planning should not remain in the technical realm but must be elevated to executive-level discussion. “The conversation shifts from abstract considerations of cyber risk to addressing how to protect transaction settlement systems against malware or strengthen cross-border payment authorisation processes to mitigate fraud risks,” Ukpabi explained.
Ukpabi also underscored the role of real-time analytics, particularly as open banking, digital platforms, and cloud migration expand attack surfaces. “Digital threat actors exploit speed — the faster they can penetrate systems, the more damage they can inflict before detection. Institutions must match or surpass that speed with AI-driven monitoring tools, anomaly detection systems, and automated incident response workflows. An alert should move from detection to remediation within minutes, not days.”
She added that analysing near-miss incidents or transaction anomalies could guide proactive investment in additional security measures and regulatory compliance.
Beyond technology, Ukpabi stressed that cybersecurity resilience depends on organisation-wide collaboration. “A compliance officer who understands threat trends can better craft internal policies; a branch manager trained in early fraud recognition can escalate red flags faster; a technology lead attuned to business impact can design controls that balance security with customer experience. The risk-based model thrives where communication lines are open and silos are dismantled.”
She urged institutions to extend this cooperation to external partners, including correspondent banks, fintechs, and cloud providers. “Risk-based strategies must include robust third-party risk assessments, contractual security obligations, and shared threat intelligence networks. Digital threats evolve too rapidly for any one institution to address in isolation; coordinated defense is our most powerful collective asset.”
Ukpabi concluded that adopting risk-based approaches will not only strengthen cybersecurity but also build customer trust in a sector under constant digital pressure.
A graduate of Hult International Business School, with Master’s degrees in Finance (Boston) and International Business (London), Ukpabi has advised both multinational and nonprofit organisations on compliance, financial modelling, and risk management.