 Follow Us on Google News


 Follow Us on Google Discover
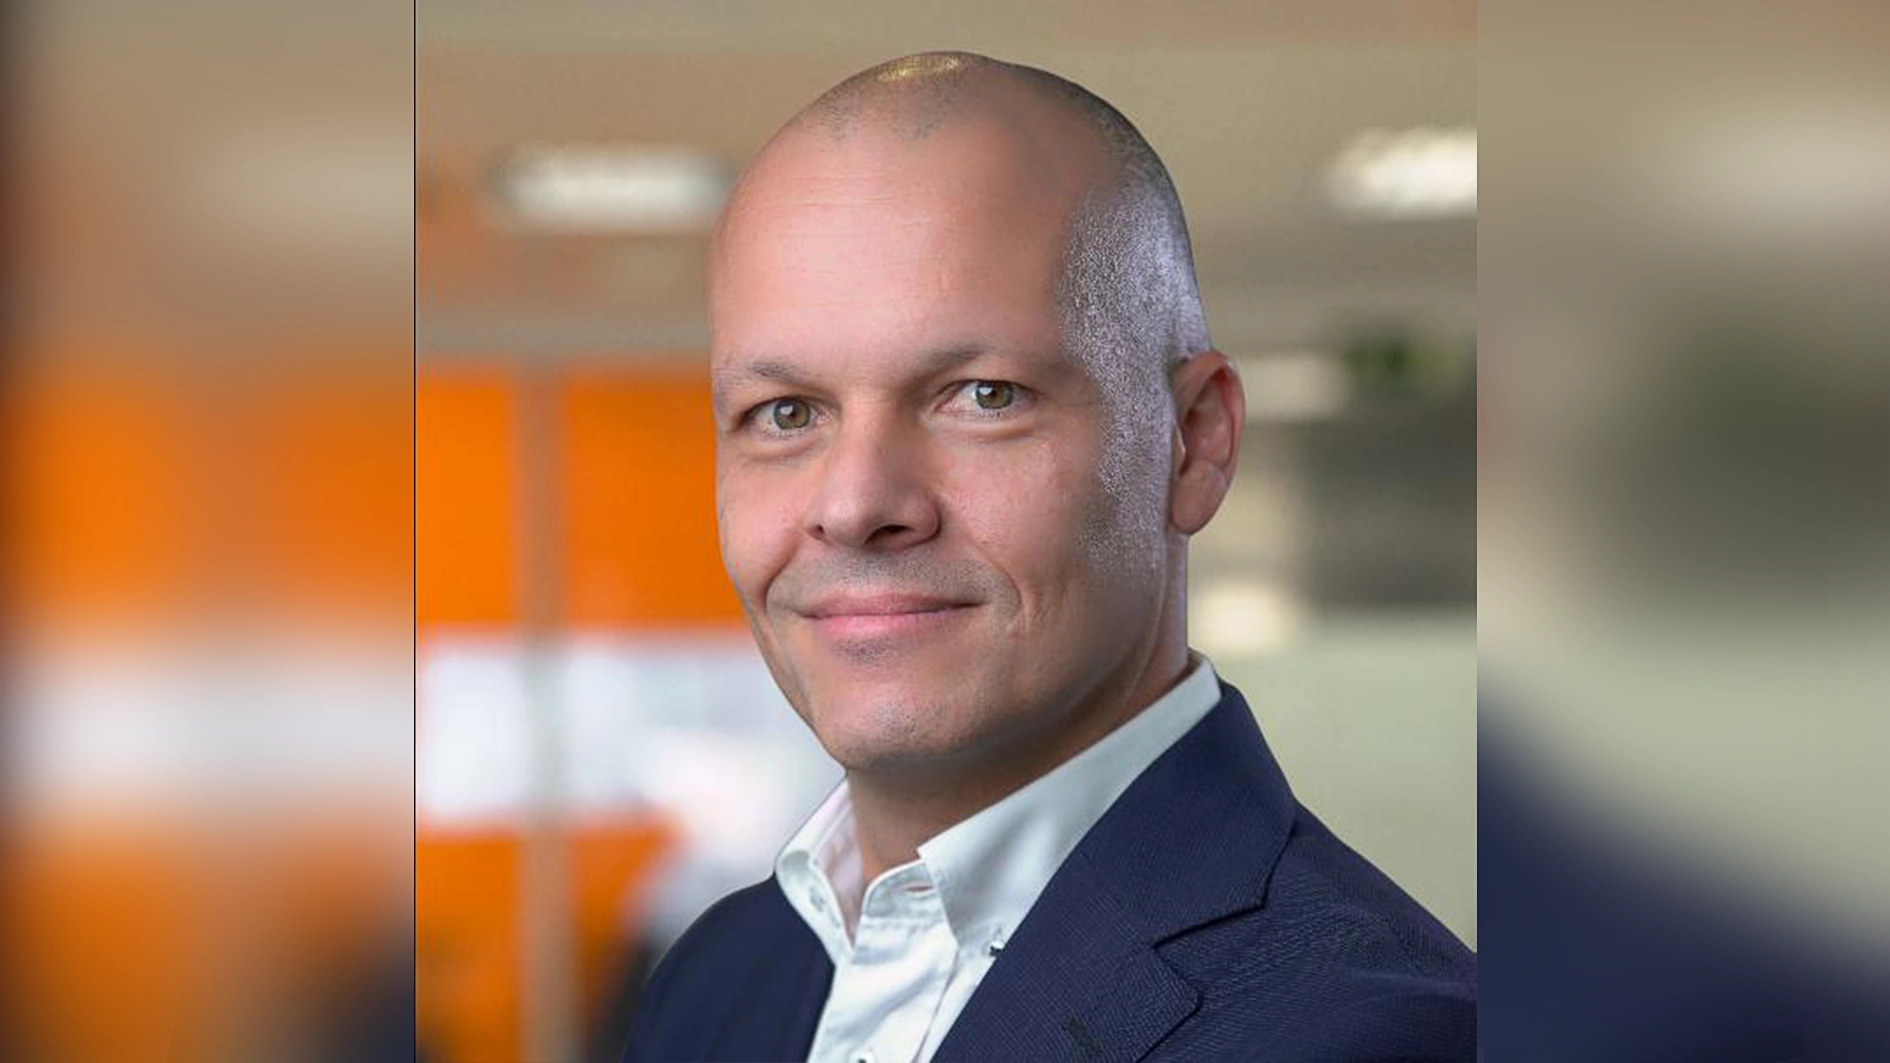
Eric Schifflers is the Group CISO and Head of GRC, TeKnowledge. In this interview with TOBI AWODIPE to mark Cybersecurity Awareness Month, he talks about why building trust in cybersecurity is important, how Nigeria can support safe digital adoption and how businesses can build digital resilience among other issues.
Nigeria’s digital economy is growing, with more people and organisations relying on digital payments, cloud platforms and mobile applications. How would you describe the cybersecurity landscape, and why is trust so important?
Nigeria has tremendous digital opportunity, but growth also expands the potential risk and attack surface. More people, businesses and public institutions are using digital payment applications, cloud platforms and mobile applications, and these services are increasingly connected. Cybercriminals follow that activity.
Organisations not only need to pay close attention to traditional methods of attack such as phishing but also the human aspects like social engineering, identity and credential theft, and business email compromise.AI can enable attackers to operate faster, scale social-engineering campaigns and make fraudulent communications more convincing. The challenge is not only that threats are becoming more advanced, but that they can also become more successful.
Nigeria needs a coordinated approach to cyber resilience, with close collaboration between the public and private sector players like TeKnowledge, where we have a full range of cybersecurity services such as managed security operations centre, vulnerability management as a service, threat intelligence and more. In essence, digital growth creates tremendous opportunity but also brings new responsibilities and risks and protecting users and data nationwide is a shared journey.
Talking about AI, as organisations adopt AI, cloud and other emerging technologies, how can they balance innovation with security?
The choice is not between innovation and security. The goal is secure innovation. Strong security enables organisations to innovate with greater confidence.
It starts with understanding the business purpose and establishing the right foundations. Organisations need to know where data will be processed, who can access it, and what happens if a technology fails or is compromised. For AI adoption, organisations need a mature cybersecurity programme covering identity management, secure configuration, encryption, monitoring and backups. They must also understand the responsibilities shared between the organisation, its users and the AI systems they use. Governance should account for applicable laws and regulations. For AI adoption, organisations need a mature cybersecurity and governance programme covering identity, secure configuration, data protection, monitoring, resilience and human oversight. They must also understand the responsibilities shared between the organisation, its users and its technology providers. Regulation is increasingly important. In the European Union, for example, the AI Act applies a risk-based framework, with obligations varying according to the organisation’s role and the nature and risk level of the AI system.
What responsibility do employees have in building a stronger cybersecurity culture, and how can organisations improve awareness without obstructing productivity?
People can be a strong line of defence, particularly as AI changes the threat landscape. Employees should be able to report security incidents or suspicious activity easily and without hesitation. A strong cybersecurity culture recognises that employees are not simply the weakest link; they are an essential part of the defence. They need to follow security policies, protect their credentials, verify unusual requests and report suspicious activity quickly. Organisations, in turn, must make secure behaviour practical, understandable and repeatable. Annual security awareness training is no longer sufficient on its own. Organisations need continuous, role-based guidance that reflects changing threats, technologies and working practices. Organisations should provide short, relevant and continuous guidance based on situations employees actually face. Finance teams, for example, need to understand payment fraud; executives need to recognise impersonation attempts and deepfakes and technical teams need to follow secure development practices. Other employees should know how to identify and report phishing. The goal is not to turn every employee into a cybersecurity expert. It is to help people make safer decisions and know when to seek advice or assistance.
What role does leadership play in making cybersecurity a business priority rather than treating it solely as an IT responsibility?
Cybersecurity capabilities may be operated day to day by specialist teams, but cyber risk is a business risk. Executive leadership and the board are responsible for ensuring that it is understood, governed and managed within the organisation’s risk appetite. Leadership determines whether cybersecurity becomes a business priority or remains isolated within the IT or technical department.
Executives do not need to become technical specialists, but they do need to understand the risks and how a cyber incident could affect services, data and the organisation’s ability to meet its commitments to customers and other stakeholders. They need to know what could interrupt those services, how the organisation would respond and how quickly it could recover. Cybersecurity and information security teams also need to explain risk in business terms, such as operational disruption, customer impact, financial loss and regulatory exposure. This helps boards and executive teams make informed decisions and understand their accountability for risk.
From a Nigerian perspective, what needs to happen at a wider ecosystem level to support safe digital adoption?
It starts with a clear national vision. Countries want to improve citizens’ lives through digital adoption, safe access to services and wider internet access. But new opportunities also bring new risks.
Nigeria should continue strengthening and harmonising its regulatory and policy framework, building on existing legislation and institutions while ensuring that guardrails remain clear, practical and supportive of innovation. Government has an important role in creating rules that help organisations understand what is expected of them and give people confidence to embrace new technologies. The public and private sectors also need to work together, including with technology providers like TeKnowledge, to support the safe adoption of AI, cloud, mobile services and other emerging technologies.
What practical steps should Nigerian organisations prioritise over the next 12 months to strengthen cyber resilience and build trust?
There are five areas I would prioritise.
First, identify critical assets and services. Organisations cannot protect everything in the same way. They need to understand which services are essential and establish appropriate minimum controls and safeguards. At a national level, this includes critical services such as banking, water, electricity, oil and gas, and healthcare. Second, strengthen digital identity. Organisations need confidence that the person accessing a service is who they claim to be. This means applying strong identity security practices, including multi-factor authentication and least-privilege access.
Third, improve basic cybersecurity hygiene and maintain an adaptable security programme. Organisations need visibility of their IT and operational technology assets through a complete asset inventory.
Fourth, strengthen vulnerability management and secure configuration. The number of vulnerabilities being identified is growing, and organisations need to address weaknesses, particularly in internet-facing systems, quickly.
Fifth, improve detection, response and recovery. The question is no longer simply whether an organisation will experience a security incident, but when it might happen and how quickly the organisation can detect it, respond and recover.
How can organisations make sure cybersecurity keeps pace with AI and other rapidly evolving technologies?
Safe AI adoption is a journey, not a one-off exercise. Organisations need to adapt as quickly as the technology evolves. At TeKnowledge, we have developed a safe AI adoption programme. One of its pillars is enabling trust. That includes upskilling and training, starting with leadership so executives understand the technology, the terminology and the risks. Once leaders understand how AI can help an organisation work better, move faster, reduce costs and remove manual work, they are better placed to make informed decisions about its adoption. Organisations do not have to do this alone. Government and businesses can work with subject-matter experts and technology providers to support the journey.
What is your final message to Nigerian business leaders about building digital resilience?
Building digital resilience requires shared responsibility. AI is transforming organisations across sectors, but the question is how to embrace it safely and securely. Organisations need to keep learning and adapting, and they should work with the right experts rather than trying to navigate every challenge alone. Trust, training and collaboration are important foundations for safe technology adoption. This is an ongoing journey that will continue to evolve alongside technology.